
ROI of AI 2026
Enterprise AI rapidly went from pilot to production to value. Now organizations are measuring AI’s value against its costs. The question is where does AI deliver the greatest financial returns?
Read →
Enterprise AI rapidly went from pilot to production to value. Now organizations are measuring AI’s value against its costs. The question is where does AI deliver the greatest financial returns?
Read →
Organizations are reshaping business operations and unlocking workforce performance with GenAI. In fact, 90% of business leaders believe that these productivity gains could even reduce employee stress and burnout. Read this guide to discover how you can implement a GenAI solution that empowers your employees at every level to speed up case research and resolution, […]
Read →
New technology brings new opportunities. It also brings hype,”fear of missing out,” and disappointment. AI is proving to be no exception to this rule. So the questions that many of us are currently considering include “What is AI really?”, “Can it help us succeed?” and “Are we missing out?” Download this guide from author and […]
Read →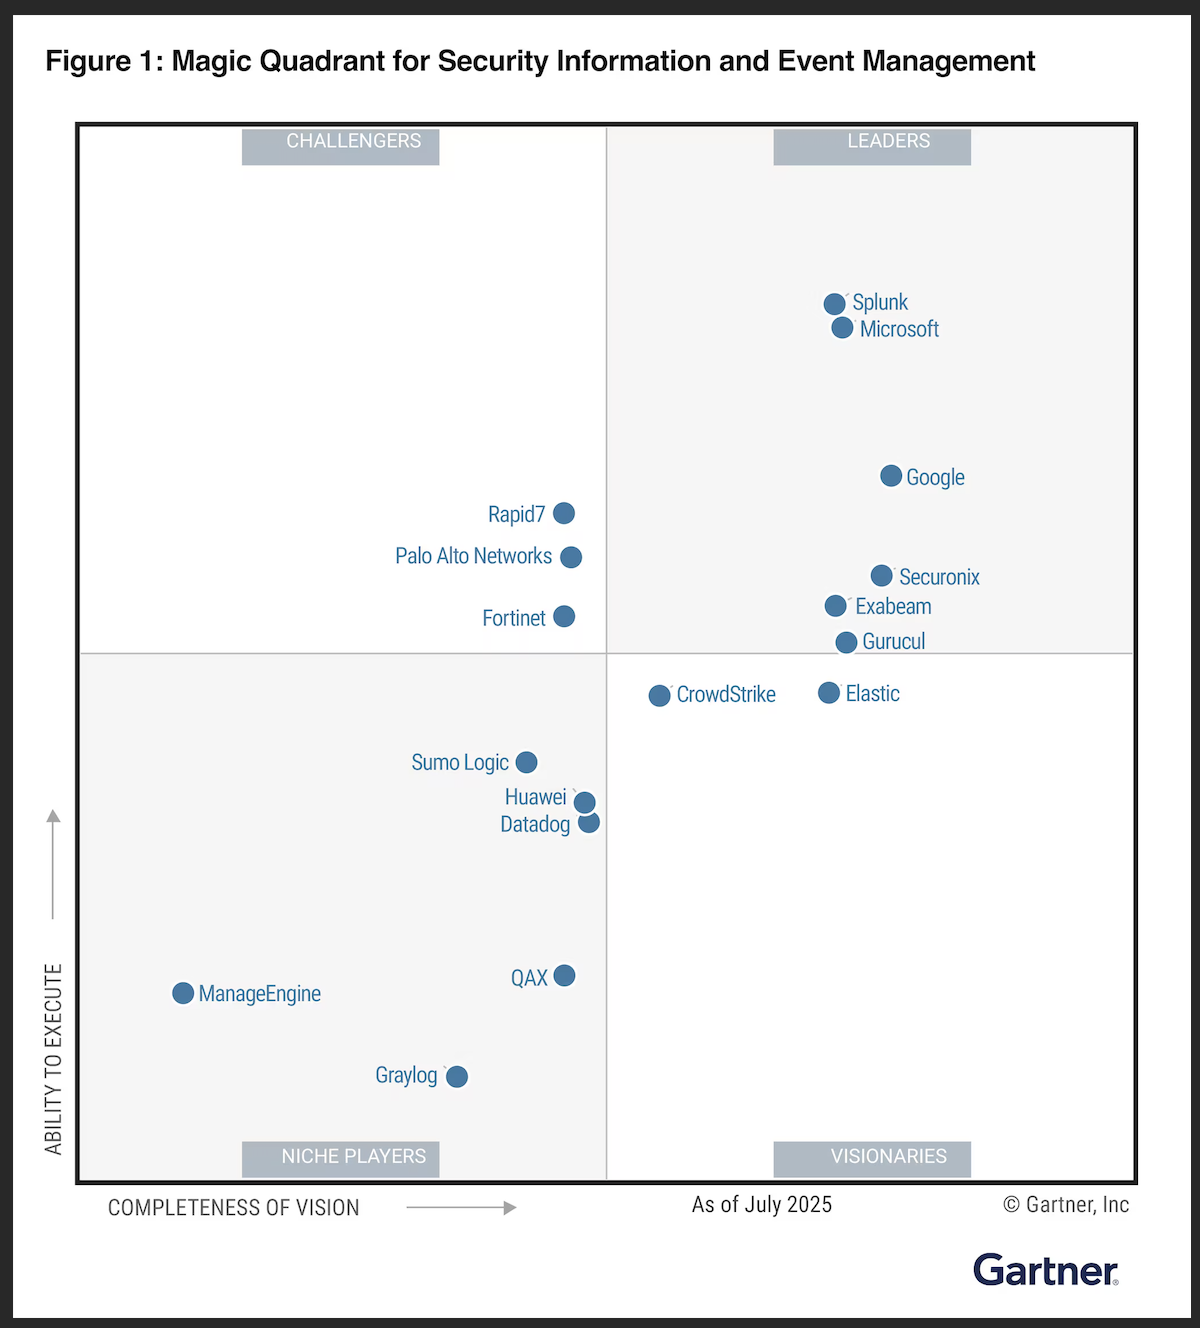
Splunk named a Leader 11 times in a row. For the eleventh consecutive time, Splunk is proud to be named a Leader in the 2025 Gartner Magic Quadrant for Security Information and Event Management (SIEM). Gartner defines SIEM as a configurable system of record that collects, aggregates and analyzes security event data from on-premises and […]
Read →
IT operations have never been more complex with distributed architectures, hybrid and multi-cloud environments, and relentless digital demands push teams to their limits. Siloed tools, exploding data volumes, and blind spots slow detection and resolution, while rising costs and strict compliance mandates increase the pressure. The Splunk Platform is purpose-built to help ITOps teams overcome […]
Read →
Transform your IT operations with a unified data platform that consolidates metrics, logs, and traces for faster incident detection and resolution. Gain real-time visibility, reduce alert noise, and leverage AI-driven insights to proactively manage your infrastructure. Empower your team with seamless collaboration and secure, compliant data management. • Ingest and index all data types once […]
Read →
Organizations rely on threat hunting to identify malicious activity, improve security and mitigate risk. The PEAK Threat Hunting Framework — a practical, vendor-agnostic, customizable approach to threat hunting, designed to help organizations create or refine their threat hunting programs — takes the experience of top threat hunters and translates their insights to help you gain […]
Read →
So it’s time to replace your SIEM — what now? Replacing a SIEM is a major decision for an organization. The decision to do so is usually the result of a combination of factors including product functionality, cost and vendor relationship. And now more than ever, best-in-class security operations require a modern SIEM solution that […]
Read →
Splunk was ranked first in every Use Case in the 2025 Gartner® Critical Capabilities for Security Information and Event Management report. The report assessed SIEM capabilities for three different Use Cases (Out-of-the-Box SIEM, Customizable SIEM and Threat Detection, Investigation, and Response) against the increasingly complex vendor landscape. Download the latest Gartner report to discover:• Why Splunk […]
Read →
As customer and business demands accelerate, site reliability engineers, ITOps teams, developers and management need operational visibility into their entire architecture. But complex modern infrastructure and applications make answering questions about what happened, who was affected and how it can be fixed more difficult than ever. Observability systems enable you to inspect and understand your […]
Read →
Today’s most damaging breaches don’t start with malware alerts: They start with misconfigured identities, exposed APIs, and AI-assisted attacks that move faster than ever. That’s why we created Top 50 Cybersecurity Threats: a definitive guide to the threats that matter now — and how they unfold in modern, hybrid environments. Download the latest edition to […]
Read →